> Source: [sk171342](https://support.checkpoint.com/results/sk/sk171342)
# sk171342 - How to restore the VPN connectivity after January 1st 2021 using Capsule VPN
| Property | Value |
|----------|-------|
| Solution ID | sk171342 |
| Date Created | 2021-01-01 |
| Last Modified | 2021-01-04 |
| Technical Level | General |
| Products | Endpoint Security |
| Versions | Cloud, E89.X, E88.X, R82.x, R82.20, R82.10, R82, R81.20 |
## Solution
Background
----------
The Capsule VPN plugin for Windows 10 initiates a VPN connection to the corporate Security Gateway. It uses the existing Endpoint Security Client configuration.
When the client establishes the VPN connection, a patch to the Endpoint Security Client can be provided using a mass deployment tool.
**Note** - If you do not have a license for Capsule VPN, contact support for a temporary license.
Administrator workflow:
-----------------------
Click Here to expand the Entire article
1. Configure the Security Gateway to enable the Capsule VPN plugin for Windows.
2. Prepare the [EPPatch.msi](https://supportcenter.checkpoint.com/supportcenter/portal?action=portlets.DCFileAction&eventSubmit_doGetdcdetails=&fileid=111732)file for distribution with your preferred tool (GPO, SCCM, etc.).
For more information on how to configure GPO see [sk171338](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk171338).
3. Instruct the end-users to download the [recovery tool](https://supportcenter.checkpoint.com/supportcenter/portal?action=portlets.DCFileAction&eventSubmit_doGetdcdetails=&fileid=111805) and install it.
### Configure the Security Gateway to enable capsule VPN:
1. From the **Gateways \& Servers** tab, double-click the VPN Security Gateway.
2. In the **VPN Clients** settings, check the **Mobile Devices - IOS and Android Clients** checkbox
* Show / Hide Example

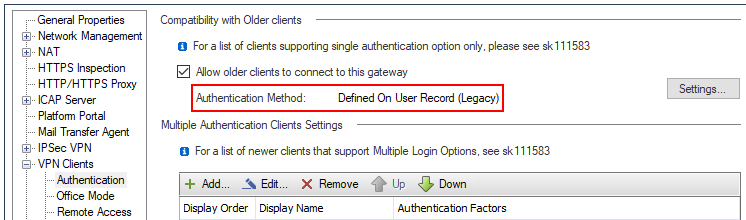
3. Set the **Authentication Method** In the **VPN Clients** \> **Authentication** \> **Compatibility with Older clients** to: **Defined on User Record (legacy)** :
* **Note** - The **Username and Password** or the **Personal Certificate**authentication methods can be set, depending on the organization's policy.
* Show / Hide Example
4. Select the **Office Mode** tab and Click the **Optional Parameters** button to configure the DNS setting for the clients to allow connectivity to the domain controller:
* Show / Hide Example

5. Open the menu from the top left corner of the SmartConsole and select **Global properties** .
6. Expand the **Remote Access** tab \> **SSL Network Extender** and change the **User authentication method** to Mixed:
* Show / Hide Example

7. Install policy.
Capsule VPN plugin for Windows 10 requires Mobile Access blade license on the gateway. By default any Security Gateway includes the license which allows 5 concurrent VPN connections from Capsule VPN clients.
In case you need more concurrent connections, you may generate Mobile Access Evaluation License ([sk102029](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk102029)) or [contact Check Point Support](https://www.checkpoint.com/support-services/contact-support/).
### Instructions for Administrators to send to end-users using certificates for authentication:
Show / Hide this section
If your VPN configuration utilize personal certificates for authentication, you may need to supply additional instructions for your users how to run the recovery tool.
1. Install recovery tool. Wait until you see the following message:
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end1202101031514361.png "Click the image to see it in full size in a new tab/window")
Note the name of VPN site "b1sa20avr.local.cp". In your organization the name of site will be different.
2. Open Windows Start menu and launch the "Settings" application.
3. In the "Settings" application search for "VPN Settings":
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end3202101031515132.png "Click the image to see it in full size in a new tab/window")
On some Windows versions prior Windows 10 "Redstone 5" you might need to search for "Change virtual private networks (VPN)":
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end3202101031515453.1.png "Click the image to see it in full size in a new tab/window")
4. Select your VPN site, and click the "Connect" button:
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end4202101031516184.png "Click the image to see it in full size in a new tab/window")
5. Select your personal certificate:
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end5202101031516465.png "Click the image to see it in full size in a new tab/window")
6. VPN connection is established when you see the "Connected" message:
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171342/end6202101031517156.png "Click the image to see it in full size in a new tab/window")
### Instructions for end-users:
1. Download the recovery tool.
2. Run the recovery tool, double-click the downloaded file.
### Limitations:
1. This workaround applies **only** to **Windows 10** 32/64 bit machines.
2. This workaround applies only for Endpoint Security VPN clients that use these authentication methods -
* One-factor authentication:
* username/password
* CAPI certificate **only**(p.12 certificates cannot be used)
* Two-factor authentication:
* Certificate, username/password
3. If other authentication methods such as SmartCards, RADIUS, etc., are in use, the workaround may not work.
**Note** - Capsule VPN plugin for Windows contains a smaller set of features than the standalone Remote Access VPN clients and Endpoint Security Clients. It may not work for some organizations due to their specific VPN configurations.
Before distributing the VPN Recovery tool in your organization, simulate the corporate computer issue by installing the VPN Recovery tool, make sure the connection establishes with your Security Gateway. In some organizations, administrators may have to adjust the VPN settings to allow the Capsule VPN plugin for Windows to connect and authenticate users.
---
# Agent Instructions
This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.
## Navigating This Knowledge Base
- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content