> Source: [sk171338](https://support.checkpoint.com/results/sk/sk171338)
# sk171338 - How to deploy EPPatch.msi via GPO
| Property | Value |
|----------|-------|
| Solution ID | sk171338 |
| Date Created | 2020-12-31 |
| Last Modified | 2021-01-26 |
| Technical Level | General |
| Products | Endpoint Security |
| Versions | Cloud, E89.X, E88.X, R82.20, R82.10, R82, R81.20 |
| OS | Windows |
## Solution
Prerequisites
-------------
1. Verify that the *GlobalSign* root certificate is installed on your affected devices. For more information see [sk171399.](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk171399)
2. EPPatcher.msi (can be downloaded from [here](https://supportcenter.checkpoint.com/supportcenter/portal?action=portlets.DCFileAction&eventSubmit_doGetdcdetails=&fileid=111732)).
3. Shared folder from which EPPatch.msi should be deployed.
4. [ORCA tool](https://docs.microsoft.com/en-us/windows/win32/msi/platform-sdk-components-for-windows-installer-developers?redirectedfrom=MSDN) installed in order to create a Windows Installer Transform (\*.MST) file.
ORCA tool is part of the Windows SDK Components for Windows Installer Developers (Install the "MSI Tools" from the SDK).
Creating MST installer file
---------------------------
1. Open ORCA tool.
2. Pull the 'EPPatcher.msi' file to the ORCA tool.
3. Select **New Transform** from the **Transform**menu.
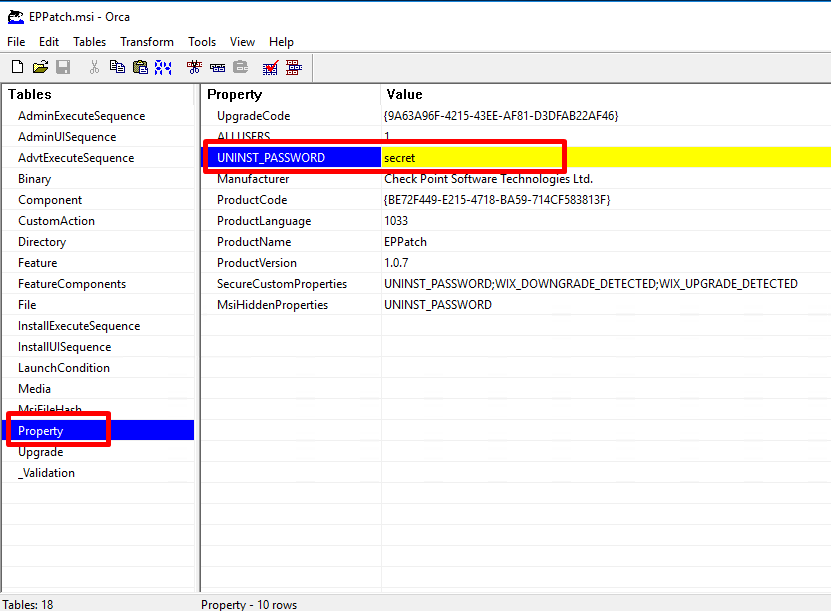
4. In **Tables** column, select **Property**.
5. On the right panel, populate **UNINST_PASSWORD** property value with the Endpoint uninstall password of your organization.
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171338/gpo1202012311615471.png "Click the image to see it in full size in a new tab/window")
6. After applying the change, select **Generate Transform** from the **Transform** menu. You will then be required to save the change as an .MST file.
Deploying EPPatch.msi via GPO
-----------------------------
1. Copy both 'EPPatch.msi' \& .MST files to the same location on the shared folder.
2. On the Domain Controller, open **Group Policy Management**.
3. Create a GPO for the desired group.
4. Right-click on the newly created GPO and select **Edit**...
5. In the new window, under **Computer Configuration** , expand **Policies** ? **Software Settings** .
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171338/gpo2202012311622042.png "Click the image to see it in full size in a new tab/window")
6. Right-click on **Software installation** ? **New** ? **Package**...
7. In the opened browser windows, select the EPPatch.msi file from the shared folder, then **Open** .
NOTE: It is essential that you use the UNC path of the shared folder.
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk171338/gpo3202012311624533.png "Click the image to see it in full size in a new tab/window")
8. In **Deploy Software** window, select **Advanced**, then Ok.
9. In **EPPatch Properties** window, select the **Modifications**tab.
10. Click **Add**...
11. Select the MST file, then click **Open**.
12. Click **OK**.
13. The GPO is ready. For the GPO to take effect, client machines should be
rebooted.
How to make sure that EPPatch.msi was successfully installed
------------------------------------------------------------
1. In "*C:\\Windows\\System32\\drivers* " you should see two files:
* epklib.bad - This is the old epklib file that was replaced by EPPatch.
* epklib.sys - This is the new file. If you right-click on it, then select
**Properties** ? **Details** tab. File version should be 8.60.5.7253.
2. In "*C:\\Windows\\Internet Logs\\EP_CDTDll.log* " you should see this line, indicating a successful patch installation:
*"File 'C:\\Windows\\System32\\drivers\\epklib.sys' dumped successfully"*
**Related solution:** [sk171275 - How to check the Patch logs for success/failure messages when using the EPPatch.msi](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk171275)
---
# Agent Instructions
This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.
## Navigating This Knowledge Base
- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content