> Source: [sk153714](https://support.checkpoint.com/results/sk/sk153714)

# sk153714 - Harmony Endpoint Learning Mode Configuration

| Property | Value |
|----------|-------|
| Solution ID | sk153714 |
| Date Created | 2019-05-21 |
| Last Modified | 2025-06-25 |
| Technical Level | General |
| Products | Endpoint Security |
| Versions | E89.X, E88.X, R82, R81.20, R81.10 (EOS) |

## Solution

### Step By Step - Web Console - Harmony Endpoint Learning mode configuration

#### Table of contents:

* Web \& Files Protection
* Behavioral Protection
* Analysis \& Remediation

|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-------------------------------------------------------------------------------------------------------------|
| **Policy Description**                                                                                                                                                                                                                                                                                                                                                                                                                                     | **Policy configuration**                                                                                    |
| **Web \& Files Protection**                                                                                                                                                                                                                                                                                                                                                                                                                                | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/web and files protection202010251325101.png)    |
| **Learning mode - URL Filtering** Set to **Detect** enable all categories on to learn about users' behavior without interrupting their work <br />                                                                                                                                                                                                                                                                                                         | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/URLF LM202010251327082.png)                     |
| **Learning mode - Download protection** Set to **Detect** During Detect mode it is good to review possible false positive detections and start excluding them                                                                                                                                                                                                                                                                                              | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Wed download LM202010251329493.png)             |
| **Learning mode - Credential protection** Set to **Prevent** Allow users to dismiss the phishing alert and access the website It is recommended to add organizational protected domains to alert about users exposing corporate credentials                                                                                                                                                                                                                | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Credentials protection LM202010251332124.png)   |
| **Learning mode - Files protection** Anti-Malware Set to **On** Anti-Malware doesn't have detect mode and it is not recommended to disable it The best option is to exclude sensitive and critical locations as first if needed Files Threat Emulation set to **On** Periodic scan every month with 4 hours interval for signatures update Allow users to cancel scan unless it has been more than 30 days since the last scan was performed <br /> <br /> | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Files protection 2 LM202010251347231.png)       |
| **Behavioral Protection**                                                                                                                                                                                                                                                                                                                                                                                                                                  | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Behavioral protection202010251348402.png)       |
| **Learning mode - Anti-Bot** Set to **Detect**                                                                                                                                                                                                                                                                                                                                                                                                             | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Anti-Bot LM202010251352113.png)                 |
| **Learning mode - Behavioral Guard \& Anti-Ransomware** Impactless focus Set to **Detect** <br />                                                                                                                                                                                                                                                                                                                                                          | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/BG AR LM202010251352544.png)                    |
| **Learning mode - Behavioral Guard \& Anti-Ransomware** Security focus set to **Prevent** It is recommended for stopping Ransomware attacks and restoring encrypted data                                                                                                                                                                                                                                                                                   | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/BG AR BP202010251355455.png)                    |
| **Learning mode - Anti-Exploit** Set to **Off**It is possible to move to Detect to get a better view of possible exploit attack and monitor them. Since it works in the exploit level it may interfere with users applications and work.                                                                                                                                                                                                                   | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Anti-Exploit LM202010251358047.png)             |
| **Analysis \& Remediation**                                                                                                                                                                                                                                                                                                                                                                                                                                | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/analysis and remediation202010251406068.png)    |
| **Learning mode - Automated attack analysis (forensics)** Enable protection set to **ON** Enable Threat Hunting set to **ON**                                                                                                                                                                                                                                                                                                                              | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/foreniscs and TH202010251441461.png)            |
| **Learning mode - Remediation \& Response** Attack remediation set to **OFF** File quarantine set to **OFF**                                                                                                                                                                                                                                                                                                                                               | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Remediation and response LM202010251441592.png) |

<br />

<br />

### Step By Step - Smart Endpoint - SandBlast Agent Learning mode configuration

**Table of Contents:**

* Anti-Ransomware, Behavioral Guard and Forensics settings
* Anti-Bot settings
* SandBlast Agent Threat Extraction, Threat Emulation, Zero Phishing and Anti-Exploit settings
* Anti-Malware settings
* Exclusions

<br />

The following section explains how to set the Learning mode configuration

* Some Action profiles have 2 modes of operation, with a focus on security or a focus on impactless policy configuration

### Anti-Ransomware, Behavioral Guard and Forensics settings {#SBA_AR_BG_F}

|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------|
| **Policy Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                        | **Policy profile configuration**                                                                                                     |
| Learning mode - Security focus **Action Profile = Triggers and automatic response** Forensics Analysis = **Always** File Quarantine = **High** Machine Quarantine = **Never** Attack Remediation = **High**                                                                                                                                                                                                                                                                                                                                                                                                                                   | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/NEW_SK_NOID1558007394134/Learning mode security focus forensics11905160459.png)  |
| Learning mode - Impactless focus **Action Profile = Triggers and automatic response** Forensics Analysis = **Always** File Quarantine = **Never** Machine Quarantine = **Never** Attack Remediation = **Never**                                                                                                                                                                                                                                                                                                                                                                                                                               | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/NEW_SK_NOID1558007394134/Learning mode Impactless focus forensics11905160502.png) |
| Learning mode **Action Profile = Monitoring and Exclusions** Exclusions are set for the **non_CP_AV certificate** Maximum Forensics Database Size on Disk = **1GByte**                                                                                                                                                                                                                                                                                                                                                                                                                                                                        | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus forensics21905210400.png)                  |
| Learning mode - Security focus **Action Profile = Attack Remediation** Malicious files = **Quarantine** Suspicious files = **None** Unknown files = **None** Trusted files = **Ignore**                                                                                                                                                                                                                                                                                                                                                                                                                                                       | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus forensics31905210400.png)                  |
| Learning mode - Impactless focus **Action Profile = Attack Remediation** Malicious files = **None** Suspicious files = **None** Unknown files = **None** Trusted files = **Ignore**                                                                                                                                                                                                                                                                                                                                                                                                                                                           | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode Impactless focus forensics31905210402.png)                |
| Learning mode **Action Profile = File Quarantine** **No default exclusions** Keep files in Quarantine for = **90 Days** Quarantine folder name = ***%ProgramData%\\CheckPoint\\Endpoint Security\\Remediation\\Quarantine\\*** Copy quarantine files to a central location = **Disabled** Allow Users to delete items from quarantine = **Enabled** Allow users to restore items from quarantine = **Enabled**                                                                                                                                                                                                                                | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus forensics41905210402.png)                  |
| Learning mode - Security focus **Action Profile = Anti Ransomware and Behavioral Guard** Anti-Ransomware and Behavioral Guard = **Enabled** Exclusions are set for: * **C:\\Windows\\explorer.exe** * **Check Point Software Technologies Ltd. Certificate** * **Non_CP_AV certificate** Backup settings: Anti-Ransomware Automatic Restore and Remediate = **Enabled** Restore to selected location = **Disabled** Anti-Ransomware Maximum Backup size on disk = **1025 Mbytes** Backup time interval = **60 minutes Note:**For Development areas it is recommended to exclude a specific folder that is used for developmental processes    | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus forensics51905210403.png)                  |
| Learning mode - Impactless focus **Action Profile = Anti Ransomware and Behavioral Guard** Anti-Ransomware and Behavioral Guard = **Enabled** Exclusions are set for: * **C:\\Windows\\explorer.exe** * **Check Point Software Technologies Ltd. Certificate** * **Non_CP_AV certificate** Backup settings: Anti-Ransomware Automatic Restore and Remediate = **Disabled** Restore to selected location = **Disabled** Anti-Ransomware Maximum Backup size on disk = **1025 Mbytes** Backup time interval = **60 minutes Note:**For Development areas it is recommended to exclude a specific folder that is used for developmental processes | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Learning mode Impactless focus forensics51905210524.png)                 |

{#limitations-Table}

### Anti-Bot Settings {#SBA_AB}

|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------|
| Policy Description                                                                                                                                                                                   | Policy profile configuration                                                                                   |
| Learning mode - Security focus **Action Profile = Blade Activation** High Confidence = **Prevent** Medium Confidence = **Detect** Low Confidence = **Detect**                                        | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus AB11905210607.png)   |
| Learning mode - Impactless focus **Action Profile = Blade Activation** High Confidence = **Detect** Medium Confidence = **Detect** Low Confidence = **Inactive**                                     | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode Impactless focus AB11905210607.png) |
| Learning mode **Action Profile = Detection Exclusions** Allow detection exclusions for following trusted entities = **Enabled** Exclusions are set for: * **Protected domains** * **Protected URLs** | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus AB21905210608.png)   |
| Learning mode **Action Profile = General Settings** Connection handling mode = **Background** Hours to suppress logs for same bot protection = **1** Days to remove bot reporting after = **3**      | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security focus AB31905210611.png)   |

{#limitations-Table}

### SandBlast Agent Threat Extraction, Threat Emulation, Zero Phishing and Anti-Exploit settings {#SBA_TE_TEX_ZP_Antex}

|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------|
| Policy Description                                                                                                                                                                                                                                                                                                                                                                                     | Policy profile configuration                                                                                          |
| Learning mode **Action Profile = Web Download Protection** Files that can be extracted and emulated = **Emulate original file without suspending access** Files that can only be emulated = E**mulate original file without suspending access** When neither extraction nor emulation is supported (Other Files) = **Allow Download**                                                                  | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex11905210611.png)   |
| Learning mode **Action Profile = Files System Monitor** Enabled monitoring = **Enabled** Default action for files written to file system = **Emulate**                                                                                                                                                                                                                                                 | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex21905210612.png)   |
| Learning mode **Action Profile = Environment Settings** Appliance Type = **SandBlast Cloud** Emulation Environments = **Use Check Point Recommended emulation environments** Upload to emulation files less than = **15 MBytes**                                                                                                                                                                       | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex31905210612.png)   |
| Learning mode **Action Profile = Inspected Domains and files** Exclusions are set for: **Protected Domains**                                                                                                                                                                                                                                                                                           | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex41905210612.png)   |
| Learning mode **Action Profile = Zero Phishing settings** Phishing protection = **Prevent Access and Log** Send log on each scanned site = **Enabled** Allow user to dismiss the phishing alert and continue to access the site = **Enabled** Allow user to abort phishing scans = **Disabled** **Note:**For Password reuse to work, please add the protected domains under the password reuse section | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex51905210613.png)   |
| Learning mode -- Security focus **Action Profile = Anti-Exploit Settings** Enable Anti-Exploit = **Enabled** Detect exploited application and log = **Enabled** Do not notify user = **Enabled** Protected Applications = **Default existing list**                                                                                                                                                    | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode security TEX-TE-ZP-Antex61905210613.png)   |
| Learning mode -- Impactless focus **Action Profile = Anti-Exploit Settings** Enable Anti-Exploit = **Disabled**                                                                                                                                                                                                                                                                                        | ![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Learning mode Impactless TEX-TE-ZP-Antex61905210613.png) |
| Learning mode **Action Profile = Static File Analysis Settings** Static File Analysis is activated in detect mode and will log file inspection                                                                                                                                                                                                                                                         | ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk153714/Static file analysis detect202006141129331.png)           |

{#limitations-Table}

### Anti-Malware configuration - use default settings {#SBA_AM}
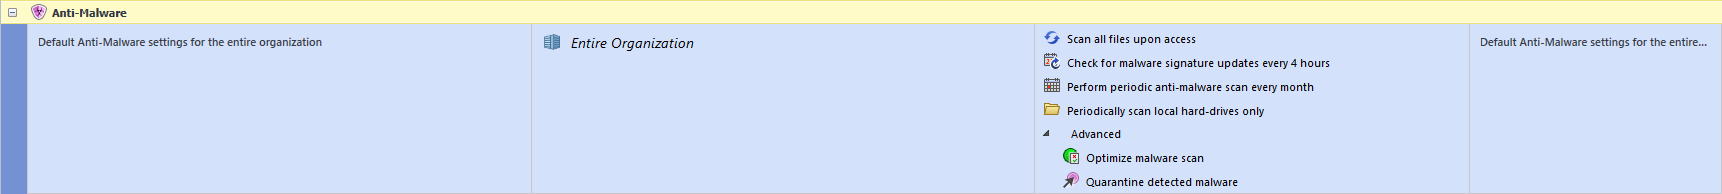
![](https://sc1.checkpoint.com/sc//SolutionsStatics/sk153714/Anti-Malware1905210653.png)

Anti-Malware doesn't have a learning mode configuration. It is either on or off. This is why it is strongly recommended to keep it active and to exclude file and folder locations according to the test/POC group findings

### Exclusions {#SBA_Exclusions}

It is recommended to create exclusions before the first deployment - through the planning phase. Exclusions can also be created through the first deployment phase on the Test/POC group of assets.

During the learning mode phase notice the following for exclusions:

1. Internally trusted processes or certified applications that create FPs or load.
2. **Do not exclude the OS (Microsoft/Apple) certificate**
3. Internally trusted and protected domains

How to exclude?

* [sk162072 - Endpoint Security Client Anti-Ransomware \& Behavioral Guard exclusion of 'Protection'](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk162072)
* For more information, see [Adding Exclusions to rules](https://sc1.checkpoint.com/documents/Infinity_Portal/WebAdminGuides/EN/Harmony-Endpoint-Admin-Guide/Default.htm?cshid=ID004).

---

# Agent Instructions

This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.

## Navigating This Knowledge Base

- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content
