> Source: [sk108074](https://support.checkpoint.com/results/sk/sk108074)

# sk108074 - SandBlast Parallel Extraction Hotfix

| Property | Value |
|----------|-------|
| Solution ID | sk108074 |
| Date Created | 2015-10-06 |
| Last Modified | 2023-01-11 |
| Technical Level | General |
| Products | Security Gateway |
| Versions | R82.10, R82, R81.20 |
| OS | Gaia |

## Solution

This article describes Threat Extraction Hotfix Accumulator - accumulation of stability and quality fixes resolving multiple issues Threat Extraction products.

[Click here](https://supportcenter.checkpoint.com//supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk108074) to see the complete article.  
**Table of Contents:**

1. Introduction
2. Downloads
3. Important Notes
4. List of resolved issues per Topic
5. Installation instructions
6. Uninstall instructions
7. Related Solutions

### (1) Introduction {#Introduction}

The **SandBlast Parallel Extraction Hotfix** for Security Gateway provides support for parallel processing of Threat Emulation and Threat Extraction, and support for SandBlast Chrome Extension.  
The hotfix includes stability and quality fixes resolving issues on Threat Extraction products.

The list below describes each resolved issue.

### (2) Downloads {#Downloads}

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| OS                   | R77.30                                                                                                                                                                           |
| Gaia - CPUSE Offline | [![](https://sc1.checkpoint.com/sc/images/download-m.png "Check_Point_Hotfix_R77.30_sk108074 (Threat Extraction)")](http://supportcontent.checkpoint.com/file_download?id=45030) |
| Gaia - Legacy CLI    | [![](https://sc1.checkpoint.com/sc/images/download-m.png "Check_Point_Hotfix_R77.30_Linux_sk108074.tgz")](http://supportcontent.checkpoint.com/file_download?id=45230)           |

Refer to section "(5) Installation instructions".

**Note:** This Hotfix is included in [Jumbo Hotfix Accumulator for R77.30](http://supportcontent.checkpoint.com/solutions?id=sk106162) - since *Take_128*.

### (3) Important Notes {#Important Notes}

* The SandBlast Parallel Extraction Hotfix can be installed on gateways with R77_30_HF5 (refer to [sk108192](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk108192)), or on a clean installation of R77.30, on Gaia OS managed by a R77.30 Management Server with [sk105412 - R77.30 Add-On](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk105412) installed.
* ***Clarification*** : SandBlast Parallel Extraction Hotfix **cannot** be installed on top of any other hotfix. **No**hotfix can be installed on top of SandBlast Parallel Extraction Hotfix.
* This hotfix is *not* supported on Security Gateways with enabled Data Loss Prevention (DLP) blade (resolved since *Take_128* of [Jumbo Hotfix Accumulator for R77.30](http://supportcontent.checkpoint.com/solutions?id=sk106162)).

### (4) List of Resolved Issues per Topic {#List of resolved issues per Topic}

|----------|----------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| ID       | Title                                                                                                                      | Description                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                |
| New Contents                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |||
| 01814720 | Adding parallel mode to Threat Emulation on MTA (Mail Transfer Agent)                                                      | When both Threat Emulation (TE) and Threat Extraction (TeX) are enabled in MTA mode, Threat Extraction-able attached files (Office and PDF) will be submitted to Threat Emulation and to Threat Extraction in parallel, and the end user will receive the converted or cleaned file, even if the emulation is in process. The original file can be accessed after Threat Emulation has completed emulation, if the file is found to be clean (configurable). **Notes:** * File types configured to skip Threat Extraction will wait for Threat Emulation to complete before being sent to the user. * If the mail has at least one non-Threat Extraction-able file (EXE, JPEG, etc), the whole mail will wait for the emulation to be completed.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                           |
| 01818120 | Support for SandBlast Chrome Extension and Sandblast Web API                                                               | Using the Web API for Threat Emulation and Threat Extraction will now support Threat Emulation+Threat Extraction integration. Original files cannot be accessed until Threat Emulation finishes scanning the document. If Threat Emulation finds the file malicious, access to the original file will be blocked. This feature is supported for requests which are sent to both Threat Emulation and Threat Extraction.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |
| Improved conversion to PDF and document cleaning                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                 |||
| 01713475 | Conversion to pdf causes files with images/barcodes to be distorted                                                        | * When converting files to pdf, images will now have dpi of 300. * To configure, edit "*scrub_convertdoc_graphic_output_dpi* " in *$FWDIR/conf/file_convert.conf*. A higher value will result in a higher quality image, and one closer to the original, but will have more performance impact on the gateway.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
| 01718973 | Improved font aliasing for better font matching by "Convert to PDF" method (improved feature)                              | * If the Convert to PDF engine does not convert documents correctly for a specific language, you can add an alias to the configuration that maps the original font name, with the font name existing on the gateway. * **It can be configured in *$FWDIR/conf/file_convert.conf* file:** > Example configuration: > ``` > : (David >      :font_original ("David") >      :font_alias ("David CLM") >      ) > ``` > This configuration means: The original document had the font "David" . The converted document will use "David CLM" every time it encounters the font "David" on the original document. > **Note:** Name aliasing should be according to the font family name. For example, if the source font name is MS Gothic (Headings Asian) in MS Office, and you choose to replace it with the "Sazanami Mincho" font, then the set ought to look as follows: > ``` > : (MS-Gothic > >           :font_original ("MS Gothic") >           :font_alias ("Sazanami Mincho") > >     ) > ``` > In order to get the family name of a font, first you should locate it (MS Office fonts are under *C:\\windows\\fonts* ) and open it with the [FontForge](http://fontforge.github.io/en-US/) software (freeware). After that, the family name of the font is under 'Element \> Font Info'. > Do the same for the Sazanami Mincho font.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                               |
| 01713626 | Conversion to PDF is poorly rendered since fonts are missing on the gateway (improved granularity)                         | If converted document fonts do not exist on the gateway, the PDF has blanks or empty squares instead of the font. To overcome this, configure the gateway to convert documents to PDF, without embedding the fonts in the PDF. **To configure it use the following procedure:** > * Change the value from "1" to "0" in the following line in *$FWDIR/conf/file_convert.conf* file: >   *:scrub_embed_fonts (0) >   ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk108074/scrub_embed1510070030.png)* > <br /> > * Kill the *scrub_file_convert* process to apply the new setting: >   *# killall -9 cp_file_convert*                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                |
| Improved support for the Chrome Threat Extraction extension                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                      |||
| 01821776 | Improved user experience when using TEX Chrome Extension                                                                   | **Note:** Currently, the Chrome extension is available as Early Availability. Refer to [sk108695](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk108695). * Improved the Threat Extraction log, generated using the Threat Extraction Chrome Extension. * Show "URL" instead of "Email Subject" inside the UserCheck Pages (only when violated by Chrome Extension) **How to Configure Smartfields in UserCheck Interaction object** > **Note:** "URL" and "Email Subject" are both Smartfields. "Email Subject" is the default. > * In SmartDashboard, you need to change "Company Policy Threat Extraction" ask page and "Threat Extraction Success Page" approve page (Go to UserCheck tab in Threat Prevention) > For those two pages consider the following: > 1. **For English language only:** When using the default Email Subject format (as appears in a default IO): >    ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk108074/Capture11510070428.jpg) >    "Email Subject: \<email subject\>" will be changed automatically to "URL: \<original url\>" (no action is required). > <br /> > 1. **For UC IO in all languages:** >    1. Insert both "Email Subject" and "Original URL" Smartfields to the UserCheck IO\* >       ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk108074/Capture21510070429.png) >    <br /> >    1. Move to Text Mode (Right-Click \> "Switch to Text Mode") >       ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk108074/Capture31510070429.png) >    <br /> >    1. Add your comments before "*$email_subject$* " and "*$orig_url$* " string, the result should be as follows: >       ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk108074/Capture41510070430.png) >       (For user's experience do not use "Email Subject:" as the Email Subject's comment) >    <br /> >    1. Save and exit. >    <br /> >    1. Install Policy. > <br /> > \* NOTE: "Threat Extraction Success Page" IO does not have an "Original URL" SmartField, it can be added manually in the Text Mode by typing: > <br /> > "*\<P\>\<SPAN id=orig_url class="smartField orig_url" contentEditable=false UNSELECTABLE="on"\>{Add your comment}$orig_url$$\</SPAN\>\</P\>"* |
| 01714845 | MTA in cluster environment is not scanning emails ([sk109198](http://supportcontent.checkpoint.com/solutions?id=sk109198)) | The hotfix should be installed on each cluster member and also on the management server. **Note:** This hotfix can be installed on gateways with R77_30_HF5 (refer to [sk108192](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk108192)), or on a clean installation of R77.30. If this hotfix is already installed, and you wish to install R77_30_HF5, then follow these steps: 1. Uninstall the *Parallel Extraction* hotfix. 2. Install *R77_30_HF5*. 3. Install the *Parallel Extraction* hotfix again.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                  |

**Note: Threat Emulation update 5 (and above) is required to run Threat Emulation using the Chrome Extension.**

### (5) Installation instructions {#Installation instructions}

* **Instructions for Gaia OS using CPUSE (Check Point Update Service Engine)**  

  * **Online installation**

    1. Connect to the Gaia Portal on your Check Point machine and navigate to ***Upgrades (CPUSE)*** pane - click on ***Status and Actions***.
    2. In the upper right corner, click on the ***Add hotfixes from the cloud*** button:  
       ![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk101975/CPUSE_Jumbo_Hotfix_Accumulator_01.png)
    3. Paste the CPUSE Identifier (***Check_Point_Hotfix_R77.30_sk108074.tgz***) and start the search.
    4. When the package is found, click on the link to add the package to the list of available packages.
    5. Select the package - click on ***Install Update*** button on the toolbar.
    6. **Machine will be rebooted automatically**.
  * **Offline installation**

    |----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
    | OS                   | R77.30                                                                                                                                                                           |
    | Gaia - CPUSE Offline | [![](https://sc1.checkpoint.com/sc/images/download-m.png "Check_Point_Hotfix_R77.30_sk108074 (Threat Extraction)")](http://supportcontent.checkpoint.com/file_download?id=45030) |

    <br />

    1. Download the Gaia CPUSE Offline package from the table above.
    2. Connect to the Gaia Portal on your Check Point machine and navigate to ***Upgrades (CPUSE)*** pane (in Gaia R77.20 and above) / to ***Software Updates*** pane (in Gaia R77.10 and lower) - click on ***Status and Actions***.
    3. On the toolbar, click on the ***More*** button - select ***Import Package*** - browse for the CPUSE Offline package (TGZ file) - click on ***Upload***.
    4. Select the hotfix package ***Check_Point_Hotfix_R77.30_sk108074.tgz*** - click on ***Install Update*** button on the toolbar.
    5. **Machine will be rebooted automatically.**

  **Notes:**
  * For detailed installation instructions, refer to [sk92449: CPUSE - Gaia Software Updates (including Gaia Software Updates Agent)](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk92449#How to work with CPUSE) - section "*(4) How to work with CPUSE*".
  * Make sure to take a snapshot of your Check Point machine before installing this hotfix.
  * Hotfix has to be installed on **all Check Point machines running on Gaia OS**.
  * In cluster environment, this procedure must be performed on *all* members of the cluster.

  <br />

  <br />

* **Instructions for Gaia/SecurePlatform OS (manual installation in Command Line)**  

  > |-------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
  > | OS                | R77.30                                                                                                                                                                 |
  > | Gaia - Legacy CLI | [![](https://sc1.checkpoint.com/sc/images/download-m.png "Check_Point_Hotfix_R77.30_Linux_sk108074.tgz")](http://supportcontent.checkpoint.com/file_download?id=45230) |

  **Procedure:**
  1. Download the relevant hotfix package from the table above, transfer the hotfix package to the machine and unpack it:  
     **`[Expert@HostName]# tar -zxvf Check_Point_Hotfix_R77.30_Linux_sk108074.tgz`**
  2. Install the hotfix:  
     **`[Expert@HostName]# ./fw1_wrapper_HOTFIX_TEX_Q_990019045_2`**   
     Note: The script will stop all of Check Point services ('*cpstop*') - read the output on the screen.
  3. **Reboot is required.**

  **Notes:**
  * Make sure to take a snapshot of your Check Point machine before installing this hotfix.
  * Hotfix has to be installed on **all Check Point machines running on Gaia/SecurePlatform OS**.
  * In cluster environment, this procedure must be performed on *all* members of the cluster.
  {#CLI_anchor_for_Mobile_App_Gaia}
{#CLI_anchor_for_Mobile_App_Gaia}

### (6) Uninstall instructions {#Uninstall instructions}

* **On Gaia OS using CPUSE (Check Point Update Service Engine)**  

  1. Connect to the Gaia Portal on your Check Point machine and navigate to ***Upgrades (CPUSE)*** pane - click on ***Status and Actions***.
  2. Select ***Installed*** in the menu near the Help icon.
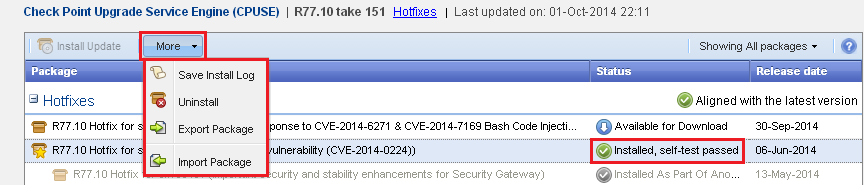
  3. Select the hotfix package ***Check_Point_Hotfix_R77.30_sk108074.tgz*** - click on ***More*** button on the toolbar - click on ***Uninstall*** .   
     *Example* :  
     [![](https://sc1.checkpoint.com/sc/SolutionsStatics/sk92449/sk92449_v705_More_button_for_Installed_package.png)](https://sc1.checkpoint.com/sc/SolutionsStatics/sk92449/sk92449_v705_More_button_for_Installed_package.png "Click the image to see it in full size in a new tab/window")
  4. **Machine will be rebooted automatically.**

  **Notes:**
  * For detailed uninstall instructions, refer to [sk92449: CPUSE - Gaia Software Updates (including Gaia Software Updates Agent)](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk92449#How to work with CPUSE) - section "*(4) How to work with CPUSE*".
  * In cluster environment, this procedure must be performed on *all* members of the cluster.

  <br />

  <br />

* **On Gaia/SecurePlatform OS (manual uninstall in Command Line)**  

  1. In command line go to */opt/CPsuite-R77/*.
  2. Run: ***# ./uninstall_fw_wrapper_HOTFIX_TEX_Q***
  3. **Reboot is required.**

  **Note:** In cluster environment, this procedure must be performed on *all* members of the cluster.

### (7) Related Solutions {#Related Solutions}

* [sk108695 - Using Check Point SandBlast Zero-Day Protection Chrome Extension through the Threat Prevention Unified API](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk108695)
* [sk115252 - Threat Emulation logs show "Detect" for e-mail attachments instead of "Prevent" when Threat Extraction blade is also enabled](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk115252)

---

# Agent Instructions

This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.

## Navigating This Knowledge Base

- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content
