> Source: [sk105318](https://support.checkpoint.com/results/sk/sk105318)
# sk105318 - How to work with Anti-Virus / Anti-Bot
| Property | Value |
|----------|-------|
| Solution ID | sk105318 |
| Date Created | 2015-03-31 |
| Last Modified | 2024-04-27 |
| Technical Level | General |
| Products | Security Gateway |
| Versions | R81.20, R81.10 (EOS), R81 (EOS) |
## Solution
Configuration
-------------
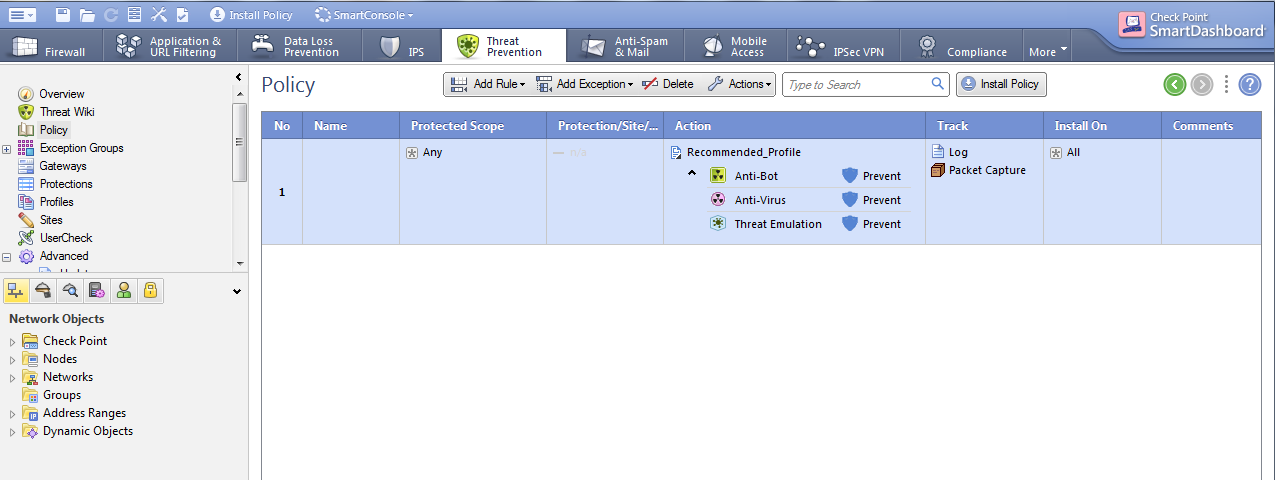
Anti-Virus / Anti-Bot default configuration and policy are very simple, intuitive and set in advance to protect the internal network in the most efficient way.
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk105318/policy11503300035.png "Click the image to see it in full size in a new tab/window")
R80.10 and higher:

Use the default policy and rule base, and these setting should not be changed. The only scenario when we need to add another rule to Anti-Virus / Anti-Bot policy is described in [sk92515 - How to configure Anti-Virus Exceptions](http://supportcontent.checkpoint.com/solutions?id=sk92515).
This is an example of incorrect policy:

R80.10 and higher:

With this setting all traffic will be matched on rule "1" and AB blade only ( no inspection for AV and TE ).
Protections
-----------
There are different Anti-Virus / Anti-Bot protections with different confidence levels and performance impacts.
The default "Recommended Profile" for Anti-Virus / Anti-Bot contains the best setup in terms of performance and reliability of detection rate.
Deviation from the "Recommended Profile" can cause performance impact on the environment and false positive detections.
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk105318/protection1503300036.png "Click the image to see it in full size in a new tab/window")
R80.10 and higher:

Check Point Threat Wiki
-----------------------
Threat Wiki contains all the current information regarding the Malware and protections.
The Threat Wiki is available in the SmartDashboard and it is an easy to use tool that lets you search and filter through Check Point's Malware Database.
Filter by a category, type or risk level and search for a keyword or malware.
Threat Wiki is also accessible online at
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk105318/Threat_Wiki1503300041.png "Click the image to see it in full size in a new tab/window")
Supported protocols
-------------------
* HTTP
* SMTP
* HTTPS (if HTTPS Inspection is enabled)
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk105318/protocol 1503300042.png "Click the image to see it in full size in a new tab/window")
Files Types feature
-------------------
This feature provides the ability to specify "safe" file types that Anti-Virus does not inspect.
You can also configure file types that the Security Gateway blocks. File types can be considered safe because they do not normally contain viruses.
For example, picture and video files are normally considered safe.
**Note:** This feature will block the file base on its type, according to the policy that was set, and not because the file is malicious.

Archives scanning
-----------------
This feature allows the customer to configure how the Anti-Virus engine unpacks and scans file archives.
**Important Note:** Using this feature together with "file types" will not provide the ability to block files types (non malicious) within ZIP files.
The ability to block non malicious files within ZIP files is not available for Anti-Virus blade. Use the Threat Emulation blade.
Traditional Anti-Virus
----------------------
Anti-Virus blade and Traditional Anti-Virus can not be activated on the same Security Gateway.
Therefore, all Traditional Anti-Virus settings should be disabled.
[](https://sc1.checkpoint.com/sc/SolutionsStatics/sk105318/T_AV1503300043.png "Click the image to see it in full size in a new tab/window")
**Related solutions:**
* [sk92264 - ATRG: Anti-Bot and Anti-Virus](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solutionid=sk92264)
---
# Agent Instructions
This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.
## Navigating This Knowledge Base
- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content