> Source: [sk100502](https://support.checkpoint.com/results/sk/sk100502)
# sk100502 - How to configure Equal Cost Multipath (ECMP) over OSPF on Gaia OS
| Property | Value |
|----------|-------|
| Solution ID | sk100502 |
| Date Created | 2014-05-01 |
| Last Modified | 2024-03-07 |
| Technical Level | General |
| Products | Security Gateway |
| Versions | R82.10, R82, R81.20 |
| OS | Gaia |
## Solution
**Table of Contents:**
1. Objective
2. Introduction
3. Configuration
4. Limitations
5. Verifying ECMP functionality
6. Troubleshooting
7. Related documentation
8. Related solutions
(1) Objective {#Objective}
--------------------------
This document describes how to setup **ECMP over OSPF** on Check Point Gaia OS.
This document focuses on the basic configuration of ECMP over OSPF and does not discuss ECMP or OSPF features in details - refer to [sk95968 - OSPF on Gaia](http://supportcontent.checkpoint.com/solutions?id=sk95968).
Before starting the ECMP over OSPF configuration, user should be familiar with underlying features and their configurations such as static and dynamic routing, ClusterXL, VRRP, SAM configuration.
It is assumed that user has basic knowledge of ECMP and routing in general and OSPF in particular.
(2) Introduction {#Introduction}
--------------------------------
* **Next Hop Selection Algorithm**
Nexthops are selected based on weighted fair queuing. Once the next hop is selected it stays the same as long as entry is in the route cache. Once the entry is deleted from route cache nexthop can change when queried for destination next time.
* **ECMP for OSPF in Gaia OS**
Check Point's OSPF routing suite supports up to ***eight*** simultaneous routes, which means that up to *eight* OSPF routes can be used for ECMP.
If the routing metric calculations discover more than eight paths of equal cost to the same destination, the ECMP feature makes available only the first eight.
* **Asymmetric Routing**
One of the issues, with which Network Administrators have to deal, is asymmetric routing through the firewalls. Problems occur when an outbound packet goes through one interface of the firewall, but the return packet is received on a different interface of the firewall.
Typically, firewalls have Anti-Spoofing drop policy on interfaces, which will drop such asymmetric packets. To solve this problem on Check Point Security Gateway, administrators can change the interface policy in the SmartDashboard in Security Gateway's object: add Destination networks to the "Specific Group of networks behind interface" for all interfaces, on which the traffic of interest is expected.
Alternately, you can allow asymmetric packets by setting the Anti-Spoofing to detecting them, or by disabling Anti-Spoofing completely.
(3) Configuration {#Configuration}
----------------------------------
Ensure the following items have been completed before attempting to configure ECMP over OSPF:
* The Security Gateway must be fully configured (including all the relevant Software Blades).
* Policy must be installed on Security Gateway (and allow the relevant traffic to pass between the involved networks).
* Basic routing should be working as expected.
* OSPF must be configured (refer to [sk95968](http://supportcontent.checkpoint.com/solutions?id=sk95968)), and OSPF neighborships should be established.
Notes:
* In ClusterXL, OSPF state is present on the Standby member.
* In ClusterXL, use cluster Virtual IP addresses and set "`virtual address`" on OSPF interfaces.
* In VRRP cluster, you can use either cluster Virtual IP addresses, or physical IP addresses on OSPF interfaces.
**ECMP for OSPF is enabled by default** , and default number of maximum paths is set to 8 (eight).
To disable ECMP for OSPF, set the number of maximum paths to 1 (one).
*Example topology*:

Procedure:
1. Set the desired number of '`Maximum Paths`' / '`Maximum Path Splits`' (either in Gaia Portal, or in Clish):
* **Either in Gaia Portal**
1. In the tree view, go to '`Advanced Routing`' pane - click on '`Routing Options`'.
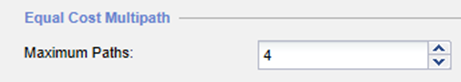
2. In the '`Equal Cost Multipath`' section, set the desired '`Maximum Paths`' value:
Notes:
* '`Maximum Paths`' specifies the maximum number of equal-cost paths to use (range: 1-8; default: 8) when multiple such paths to a destination are available.
Only OSPF, BGP, and static routes are able to use paths/routes with more than one "nexthop".
* To disable ECMP, set the number of paths to 1 (one).
* Changing this value will result in re-installing all the routes.
3. Click on '`Apply`' button.
* **Or in Clish**
1. Connect to command line on Security Gateway / each cluster member (over SSH, or console).
2. Log in to Clish.
3. Set the '`Maximum Path Splits`' value:
**`HostName> set max-path-splits `*VALUE***
Notes:
* '`Maximum Path Splits`' specifies the maximum number of equal-cost paths to use (range: 1-8; default: 8) when multiple such paths to a destination are available.
Only OSPF, BGP, and static routes are able to use paths/routes with more than one "nexthop".
* To disable ECMP, set the number of paths to 1 (one).
* Changing this value will result in re-installing all the routes.
4. Save Gaia configuration:
**`HostName> save config`**
2. **In SmartDashboard**
ECMP can cause traffic to flow asymmetrically. That is, traffic to destination may leave the Security Gateway from one interface and traffic from destination may arrive on some other interface.
Such traffic will be dropped by Security Gateway due to default Anti-Spoofing settings.
To allow the Security Gateway to receive traffic of interest on expected interfaces, destination networks of traffic of interest must be included in group of networks behind the interface, and this specific group must be applied to the interface in Security Gateway / Cluster object.
1. Create Network object for **each** relevant network.
*Based on our example - for interface eth4*:

2. Create Group object for **Internal** networks and Group object for **External** networks and add the relevant Network objects to each of the Group objects.
*Based on our example - interface eth4*:

3. Apply the Group object (that contain the relevant **Internal** networks) to the **Internal interfaces** in Security Gateway / Cluster object.
SmartDashboard - Security Gateway / Cluster object properties - '`Topology`' pane - click on '`Edit...`' - edit the Internal Interface (*in our example - eth4* ) - go to '`Topology`' tab - select '`Specific`' - select the Group object that represents the networks behind this interface - click on '`OK`'.
*Based on our example - for interface eth4*:

4. Apply the Group object (that contain the relevant **External** networks) to the **External interfaces** in Security Gateway / Cluster object.
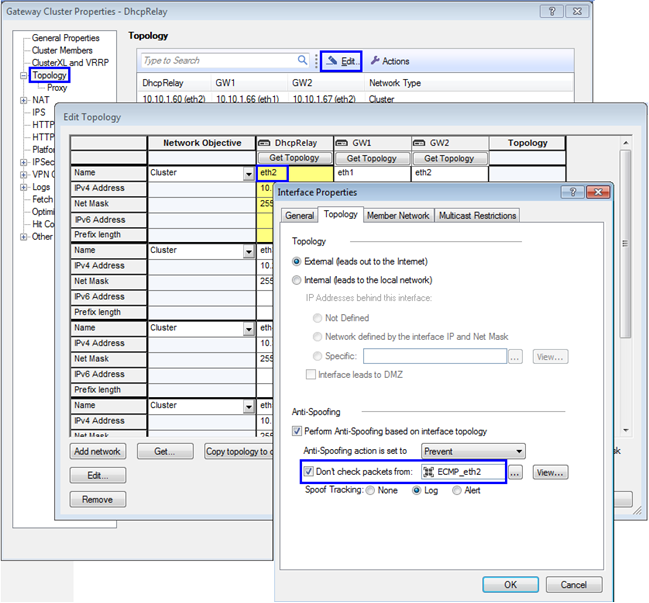
SmartDashboard - Security Gateway / Cluster object properties - '`Topology`' pane - click on '`Edit...`' - edit the External Interface (*in our example - eth2* ) - go to '`Topology`' tab - check the box '`Perform Anti-Spoofing...`' - check the box '`Don't check packets from`' - select the Group object that represents the networks behind this interface - click on '`OK`'.
*Based on our example - for interface eth2*:
5. Click '`OK`' to apply the changes and close the Security Gateway / Cluster object.
6. Create security rule(s) to allow the relevant traffic to pass between the involved networks.
*Based on our example*:

7. Install the policy on the Security Gateway / Cluster.
Alternatively, you can completely disable the Anti-Spoofing on multipath interfaces (Internal or External) in the following ways:
* Either check the box '`Perform Anti-Spoofing based on interface topology`' and in the '`Anti-Spoofing action is set to`' field, select '`Detect`':

* Or un-check the box '`Perform Anti-Spoofing based on interface topology`':

(4) Limitations {#Limitations}
------------------------------
* "Round robin" next hop algorithm is not supported.
* "Source hash" next hop algorithm is not supported.
* "Destination hash" next hop algorithm is not supported.
* ECMP over OSPF supports up to 8 simultaneous routes.
(5) Verifying ECMP functionality {#Verifying}
---------------------------------------------
* **Routing Table:**
Verify that multiple routes for equal-cost paths to the destination are correctly shown on Security Gateway / ClusterXL Active member / VRRP Master cluster member.
1. Check the Gaia OS routing table in Clish:
**HostName\> show route all**
**HostName\> show route ospf**
> *Example*:
>
> ```
> HostName> show route all
>
> C 10.110.0.0/24 is directly connected, eth5
> C i 10.110.0.0/24 is directly connected, eth5
> O H i 10.110.0.0/24 is an unusable route
> O 10.111.0.0/24 via 10.10.1.4, eth2, cost 6, age 4506
> via 10.20.1.3, eth3
> via 10.30.1.5, eth4
> C 127.0.0.0/8 is directly connected, lo
> ```
Note: In cluster, OSPF state will not be present on the ClusterXL Standby / VRRP Backup member.
2. Check the Gaia OS kernel routing table in Expert mode:
**\[Expert@HostName\]# ip route show**
> *Example*:
>
> ```
> [Expert@HostName]# ip route list
>
> 10.6.0.0/24 via 10.10.1.4 dev eth2 proto routed
> 10.111.0.0/24 proto routed
> nexthop via 10.10.1.4 dev eth2 weight 1
> nexthop via 10.20.1.3 dev eth3 weight 1
> nexthop via 10.30.1.5 dev eth4 weight 1
> 10.10.1.0/24 dev eth2 proto kernel scope link src 10.10.1.67
> ```
Note: In cluster, OSPF state will not be present on the ClusterXL Standby / VRRP Backup member.
* **Traffic routing:**
Verify that the traffic is routed according to ECMP configuration and routing table.
Capture the traffic using the **FW Monitor** (for syntax, refer to [sk30583 - What is FW Monitor?](http://supportcontent.checkpoint.com/solutions?id=sk30583)).
(6) Troubleshooting {#Troubleshooting}
--------------------------------------
[Contact Check Point Support](http://www.checkpoint.com/services/contact/index.html) for any assistance.
If traffic is not routed based on ECMP configuration as expected, then follow the steps below to identify the root cause and then correct the settings / configuration / security policy accordingly:
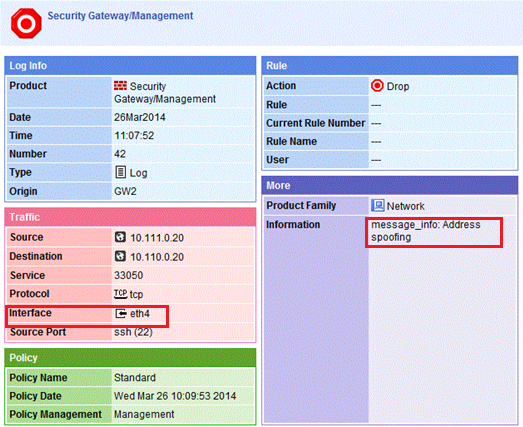
1. Check logs in SmartView Tracker. *Example*:
> 
2. Capture the traffic on Security Gateway (on the involved multipath interfaces) and on the Source Host / Destination Host.
3. Collect simple kernel debug for drops:
Prepare
>
> ```
> [Expert@HostName]# fw ctl debug 0
> [Expert@HostName]# fw ctl debug -buf 32000
> [Expert@HostName]# fw ctl debug -m fw + drop
> ```
Verify debug buffer and flags
>
> ```
> [Expert@HostName]# fw ctl debug -m fw
> ```
Start
>
> ```
> [Expert@HostName]# fw ctl kdebug -T -f > /var/log/debug.txt
> ```
Replicate the issue
Stop
>
> ```
> Press CTRL+C
> [Expert@HostName]# fw ctl debug 0
> ```
Analyze
>
> ```
> /var/log/debug.txt
> ```
> *Example*:
>
> ```
> ;[fw4_0];fw_log_drop_conn: Packet 224.0.0.5:0 IPP 89>, dropped by handle_spoofed_susp, Reason: Address spoofing;
> ;[fw4_0];fw_log_drop_conn: Packet 224.0.0.5:0 IPP 89>, dropped by handle_spoofed_susp, Reason: Address spoofing;
> ```
(7) Related documentation {#Related documentation}
--------------------------------------------------
* Gaia Advanced Routing Administration Guide ([R75.40](http://supportcontent.checkpoint.com/documentation_download?id=13221), [R75.40VS](http://supportcontent.checkpoint.com/documentation_download?id=16245), [R76](http://supportcontent.checkpoint.com/documentation_download?id=22929), [R77.X](http://supportcontent.checkpoint.com/documentation_download?id=24803), [R80.10](http://downloads.checkpoint.com/dc/download.htm?ID=54803), [R80.20](https://sc1.checkpoint.com/documents/R80.20_GA/WebAdminGuides/EN/CP_R80.20_Gaia_Advanced_Routing_AdminGuide/html_frameset.htm), [R80.30](https://sc1.checkpoint.com/documents/R80.30/WebAdminGuides/EN/CP_R80.30_Gaia_Advanced_Routing_AdminGuide/html_frameset.htm)).
* Gaia Administration Guide ([R75.40](http://supportcontent.checkpoint.com/documentation_download?id=13241), [R75.40VS](http://supportcontent.checkpoint.com/documentation_download?id=16244), [R76](http://supportcontent.checkpoint.com/documentation_download?id=22928), [R77.X](http://supportcontent.checkpoint.com/documentation_download?id=24828), [R80.10](http://downloads.checkpoint.com/dc/download.htm?ID=54824), [R80.20](https://sc1.checkpoint.com/documents/R80.20_GA/WebAdminGuides/EN/CP_R80.20_Gaia_AdminGuide/html_frameset.htm), [R80.30](https://sc1.checkpoint.com/documents/R80.30/WebAdminGuides/EN/CP_R80.30_Gaia_AdminGuide/html_frameset.htm)).
* 600 / 700 / 1100 / 1200R / 1400 Appliances Advanced Routing Reference Guide ([R75.20](http://downloads.checkpoint.com/dc/download.htm?ID=26395), [R77.20](http://downloads.checkpoint.com/dc/download.htm?ID=43085)).
(8) Related solutions {#Related solutions}
------------------------------------------
* [sk95968 - OSPF on Gaia](http://supportcontent.checkpoint.com/solutions?id=sk95968)
* [sk100504 - How to configure Equal Cost Multipath (ECMP) over eBGP on Gaia OS](http://supportcontent.checkpoint.com/solutions?id=sk100504)
* [sk92378 - Equal-Cost Multi-Path (ECMP) Routing Support on SecurePlatform](http://supportcontent.checkpoint.com/solutions?id=sk92378)
---
# Agent Instructions
This content is from the Check Point Support Center (https://support.checkpoint.com), the official knowledge base for Check Point cybersecurity products.
## Navigating This Knowledge Base
- **Complete index**: [llms.txt](https://support.checkpoint.com/llms.txt)
- **All SK articles**: [SecureKnowledge Sitemap](https://support.checkpoint.com/sitemaps/secureknowledge-sitemap-index.xml)
- **SK article URL pattern**: `https://support.checkpoint.com/results/sk/{skId}`
- **Markdown responses**: AI bot User-Agents automatically receive `text/markdown` content